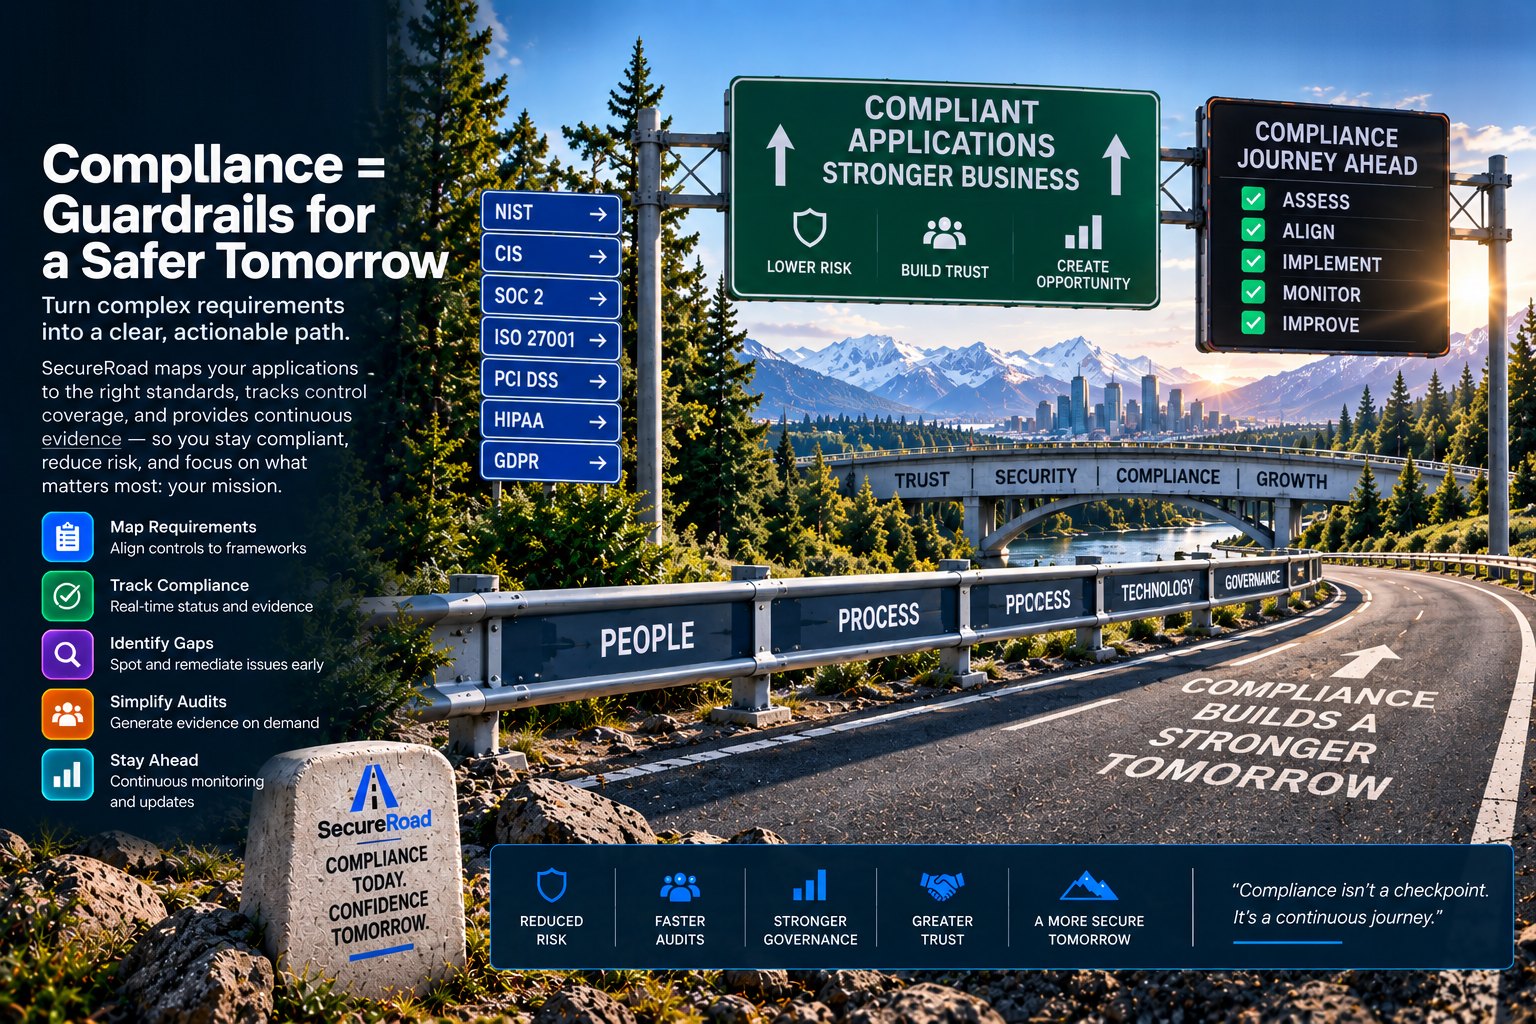
Compliance = Guardrails for a Safer Tomorrow
The cycle
Six stages, always running
Compliance never ends. It evolves.
-
1 Integrate
Connect your ecosystem.
- Link cloud, code and work tools
- Read configuration and detections
- Map evidence to requirements
-
2 Monitor
Gain real visibility.
- Collect and analyze continuously
- Detect misconfigurations and drift
- Track control status per application
-
3 Assess
Measure compliance.
- Validate controls against evidence
- Identify gaps and risks
- Unverified stays unknown, never passing
-
4 Remediate
Close gaps faster.
- Create and assign tasks
- Track progress to completion
- Validate fixes against evidence
-
5 Report
Be ready, anytime.
- Generate audit-ready views
- Keep evidence current
- Share with stakeholders and auditors
-
6 Improve
Get stronger over time.
- Track trends and metrics
- Learn from issues and audits
- Evolve your security program
Reduce riskCatch issues early.
Save timeAutomate repetitive work.
Lower costsEliminate manual effort.
Empower teamsGive ownership and visibility.
Stay aheadContinuous improvement.
Frameworks
One control model. Mapped once, answered many times.
Requirements in SecureRoad are policy written as data, not code. A framework is mapped onto them, so a control proven for one application is evidence wherever that requirement applies.
-
Requirements as policy
Every rule states its own rationale, and changes by editing policy — never by changing the engine.
-
Evidence per control
The proof behind each control, current and attributable to the application it belongs to.
-
Gaps become work
A gap is raised as work with an owner, and closes only when evidence says it is fixed.
A clearer path to compliance
Stay Ready. Move Forward.
Bring us your application count, your security stack, and your audit calendar. We'll show you where SecureRoad fits.