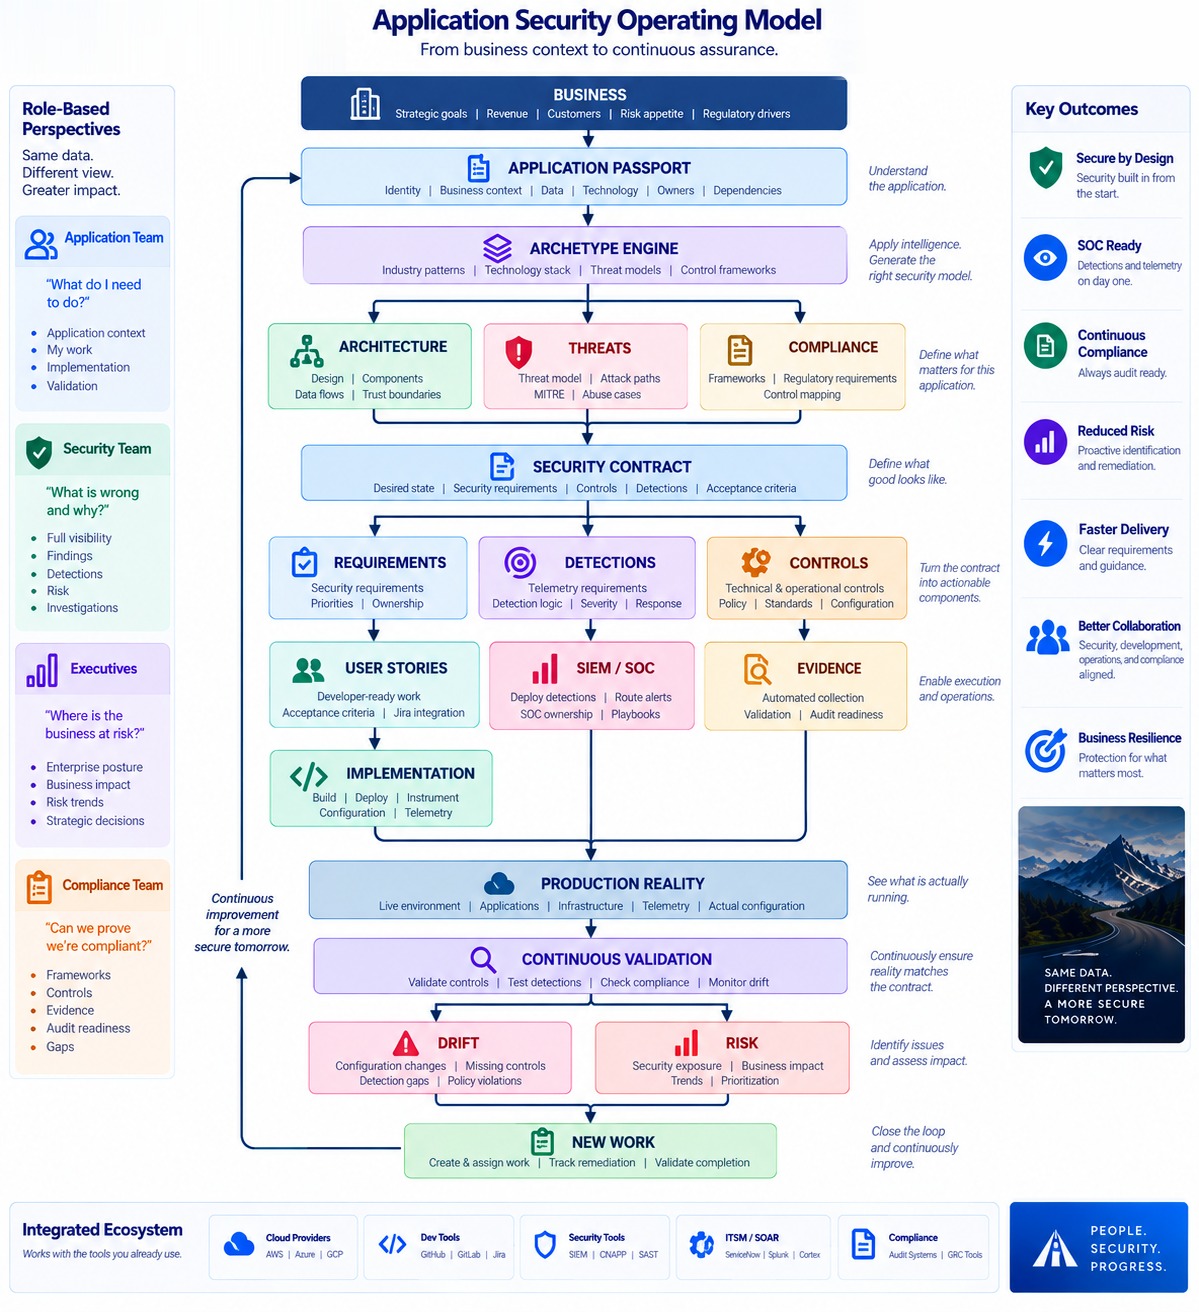
Role-based perspectives
Same data. Different view. Greater impact.
Every team reads the same record of the application, and each sees the question it is actually asking.
-
Application Team
“What do I need to do?”
- Application context
- My work
- Implementation
- Validation
-
Security Team
“What is wrong and why?”
- Full visibility
- Findings
- Detections
- Risk
- Investigations
-
Executives
“Where is the business at risk?”
- Enterprise posture
- Business impact
- Risk trends
- Strategic decisions
-
Compliance Team
“Can we prove we're compliant?”
- Frameworks
- Controls
- Evidence
- Audit readiness
- Gaps
Key outcomes
What the model produces
-
Secure by Design
Security built in from the start.
-
SOC Ready
Detections and telemetry on day one.
-
Continuous Compliance
Always audit ready.
-
Reduced Risk
Proactive identification and remediation.
-
Faster Delivery
Clear requirements and guidance.
-
Better Collaboration
Security, development, operations and compliance aligned.
-
Business Resilience
Protection for what matters most.
Integrated ecosystem
Works with the tools you already use
Naming a tool says SecureRoad reads it. It is not a claim of partnership or endorsement.
-
Cloud & infrastructure
AWS · Google Cloud · Azure · Terraform
-
Developer tools
GitHub · GitHub Actions
-
Security & SOC
Splunk · Snyk Code · Snyk DAST · CrowdStrike Falcon
-
Work & communication
Jira · Slack · Microsoft Teams · ServiceNow
Ready to connect the road?
Same road. A safer tomorrow.
Bring us your application count, your security stack, and your biggest operational pain points. We'll show you where SecureRoad fits.