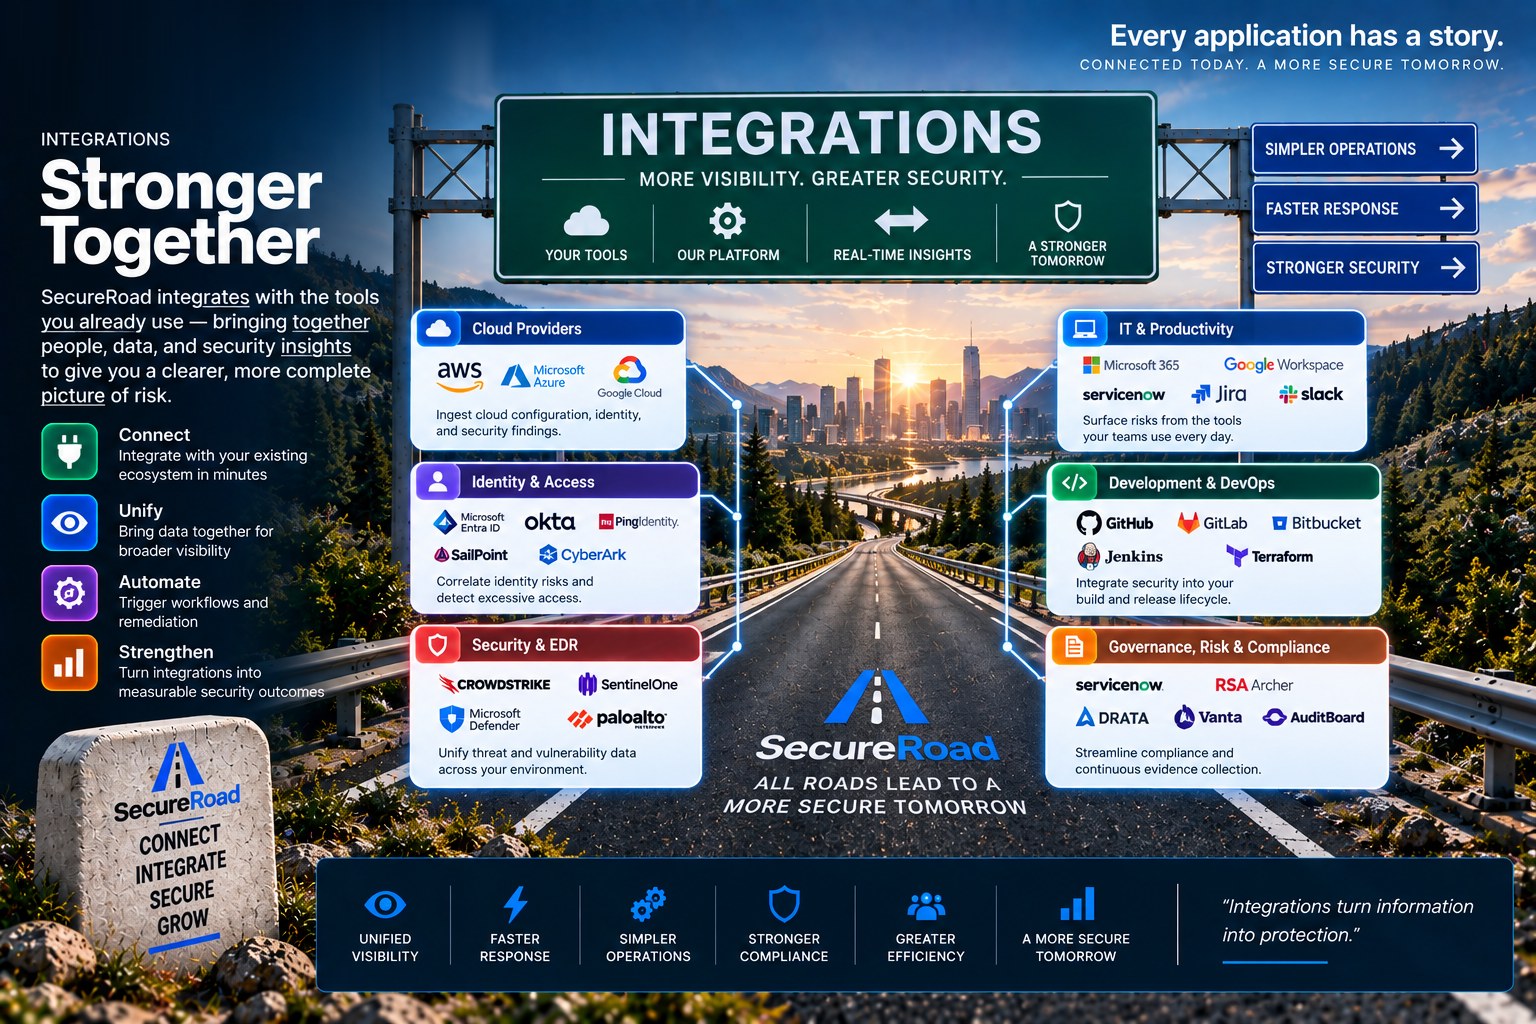
Stronger Together
The journey
From why it exists to how it runs
Every stage of the application is on the passport, each with its own state — so the next thing to do is never a guess.
-
1 Business context
Why it exists.
- Owner and business unit
- Data it holds
- What happens if it fails
-
2 Architecture
Define and design.
- Components and data flows
- Trust boundaries
- Required patterns
-
3 Controls
Implement security.
- Requirements from its archetype
- Evidence per control
- Exceptions by name
-
4 Work
Build and test.
- Critical, high and medium work
- Owners and dates
- Acceptance criteria
-
5 Production
Monitor and improve.
- Reality read from the account
- Drift raised as findings
- Nothing closes by going quiet
Customer Claims Portal
The passport's working view
12Security requirements
27Associated controls
4Open findings
0Critical issues
Compliance in scope
- SOC 2
- ISO 27001
Connected sources
- Jira
- AWS
- Google Cloud
- Azure
Recent ActivityView all
- Security review completed
- New finding detected
- Architecture updated
- Evidence uploaded
- Roadmap item completed
What it holds
One profile, continuously updated.
Identity and ownership
Who owns it, which business unit runs it, and what it is built on.
Risk and exposure
Tier, data classification, internet exposure, and what could happen if it fails.
Lifecycle
Ideation, architecture, build, testing, deployment and operations, each with its state.
Compliance
Coverage per application rather than per company.
Open work
Critical, high and medium, with owners and dates.
Evidence
The proof behind each control, current and attributable.
Ready to connect the road?
Know your application. Know the road.
Bring us your application count, your security stack, and your biggest operational pain points. We'll show you where SecureRoad fits.